Most businesses buy a firewall and consider network security done. That mindset made sense a decade ago; it doesn't hold up against attackers who now target remote access, cloud apps and identities just as often as the network perimeter. Sophos builds its security portfolio around that reality — a firewall that also stops zero-days and does network detection, a zero-trust layer that replaces VPN, detection-and-response tools for practitioners, and a 24/7 managed team for when you don't have practitioners of your own.
SNA Infotech already leads its cybersecurity practice with Fortinet and Sophos. This guide zooms into the Sophos side of that stack — what each piece actually does, how they connect to each other, and where a business our size typically starts.
It starts at the edge: Sophos Next-Gen Firewall
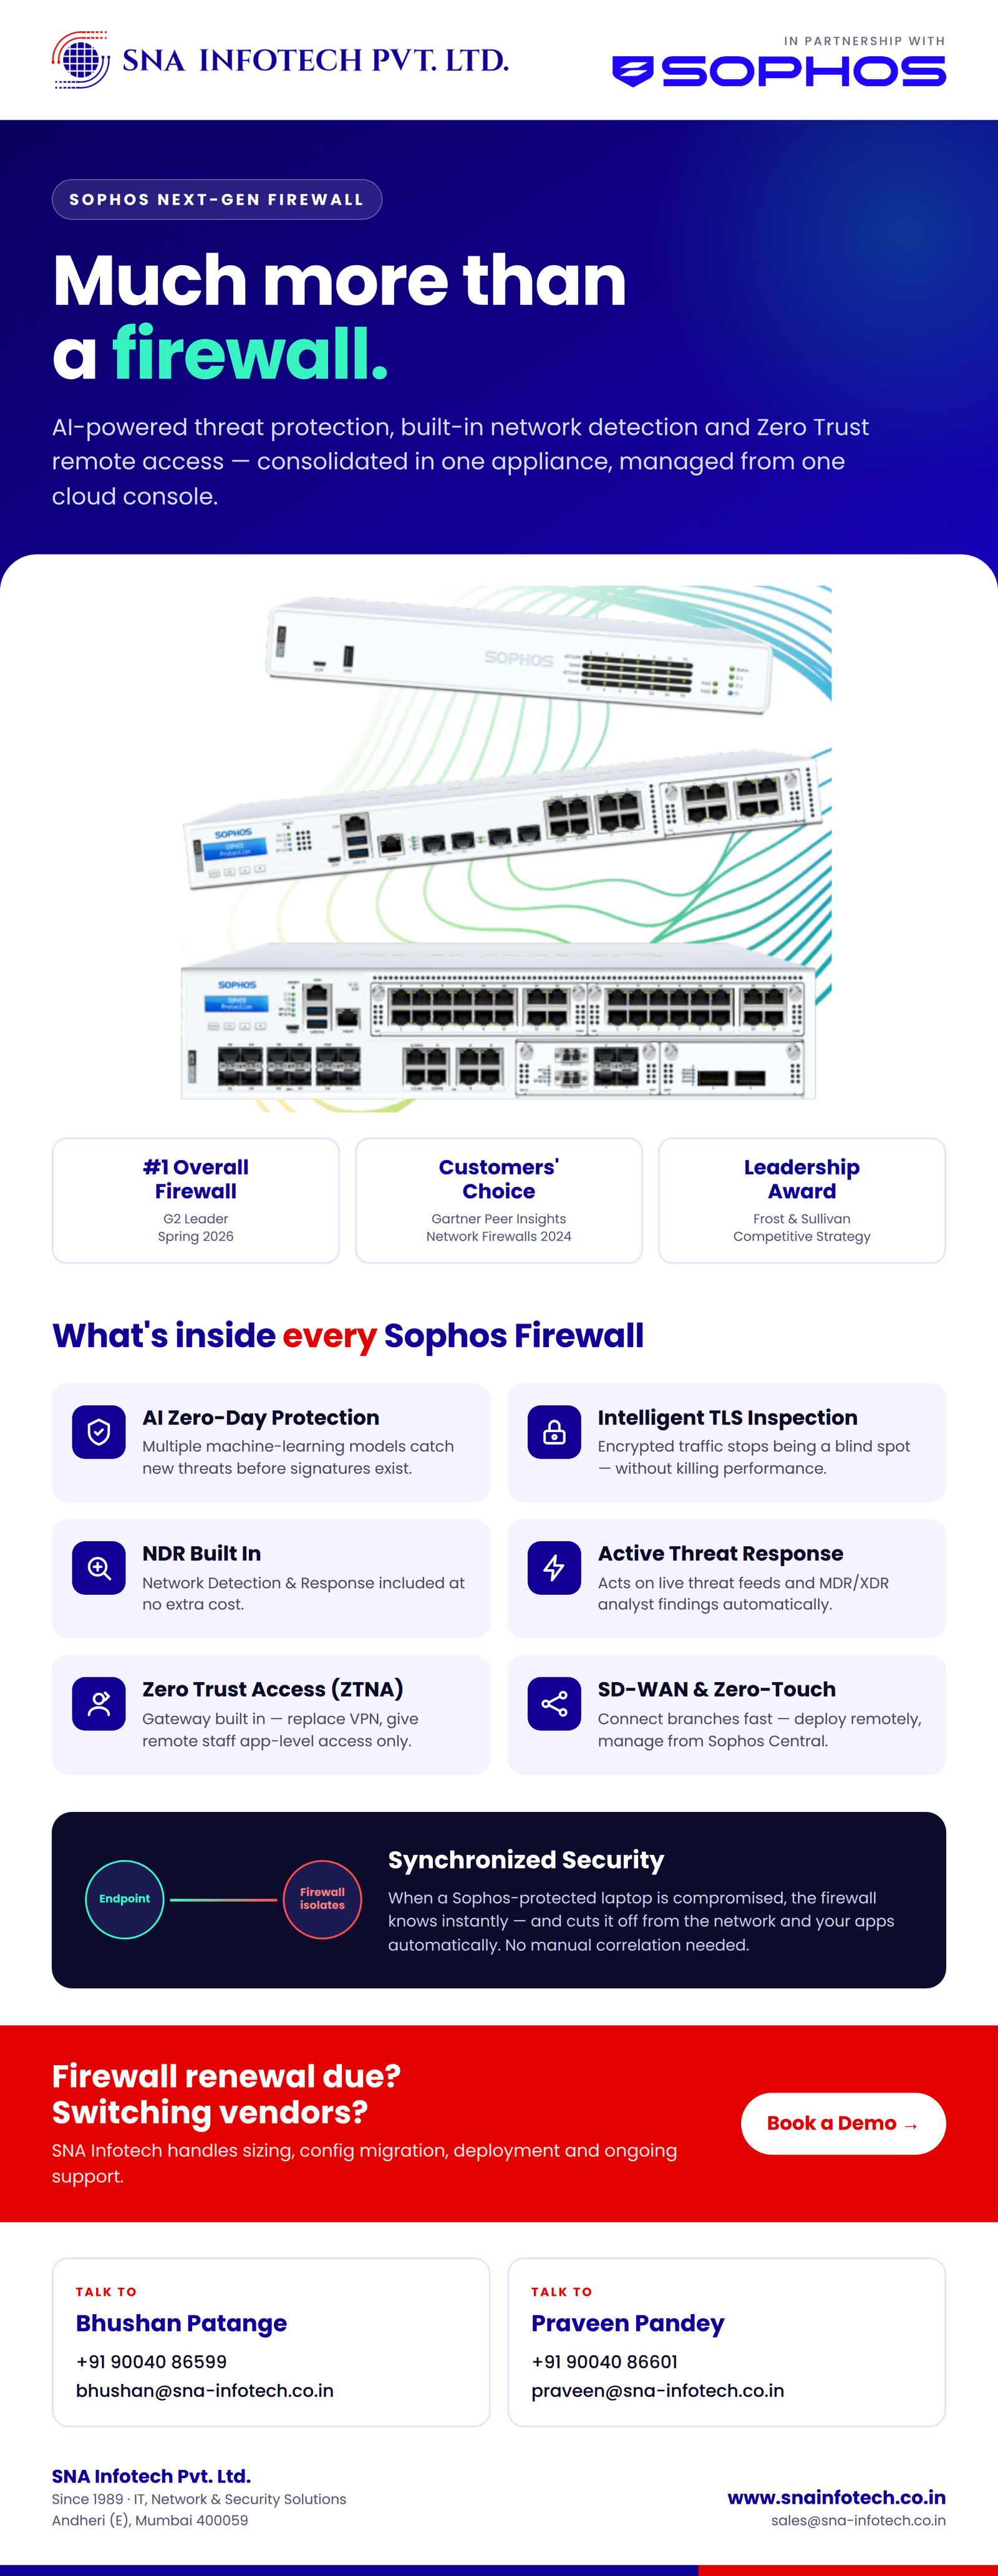
Sophos positions its firewall as more than perimeter defence — "the heart of the world's best network security platform," built to consolidate, simplify and save rather than stack up point products. Under Sophos' Xstream architecture, the XGS Series firewalls combine:
- AI-based zero-day protection using multiple machine-learning models, plus intelligent TLS decryption so encrypted traffic doesn't become a blind spot.
- Network Detection and Response (NDR) built in at no extra cost — most vendors sell this separately.
- Active Threat Response, which automatically acts on threat-intelligence feeds instead of waiting on manual rule updates.
- Comprehensive SD-WAN and zero-touch deployment, useful for multi-branch and retail-style rollouts.
- An integrated ZTNA gateway and DNS Protection — covered in the next section — so remote-access and web-filtering needs don't require separate appliances.
It's managed centrally through Sophos Central, and it's been recognised as G2's #1 overall firewall solution (Spring 2026), a Frost & Sullivan Competitive Strategy Leadership Award winner, and a Gartner Peer Insights Customers' Choice for Network Firewalls (2024).
Replacing VPN: Zero Trust Network Access, built into the firewall
Sophos' zero-trust principle is simple to state and hard for legacy VPN to match: trust nothing, verify everything. Instead of a user or device being "on the network" with broad implicit access the moment they connect, each user and device becomes its own verified, policy-based perimeter — re-checked continuously, not just at login.
In practice, this replaces the classic pain points of VPN:
- Remote workers get seamless access to just the applications they need — on-premises, data centre or public cloud — without deployment and enrolment being a full-time job.
- Ransomware and lateral movement lose their usual foothold, because a compromised device no longer has broad network reach — only explicit, policy-based access to specific apps.
- Device health is continuously checked via Sophos' Security Heartbeat, shared between Sophos Endpoint, Sophos Firewall and Sophos Central — a non-compliant or compromised device can be automatically cut off from sensitive applications.
Zero Trust Network Access now ships as a built-in gateway on every Sophos Firewall and as part of Sophos Workspace Protection, rather than a separate product line to buy and manage on its own — one less SKU to license, and one less agent to deploy.
Seeing across your whole environment: Sophos XDR
Extended Detection and Response (XDR) is built for the security practitioner who needs to investigate and respond to complex, multi-stage attacks — not just get an alert. Sophos XDR's open architecture ingests signals from endpoint, network, firewall, email, identity, backup, cloud and productivity tools (including non-Sophos products), so investigations aren't limited to what one vendor's agent can see.
Two things stand out in how Sophos has built this: an AI Assistant that lets analysts investigate in natural language — analysing suspicious commands, enriching data with threat intelligence, drafting incident reports — designed in partnership with Sophos' own frontline analysts; and AI-powered prioritisation, so a small IT team's attention goes to the handful of alerts that actually matter instead of getting buried in noise.
When you need a 24/7 team, not just a tool: Sophos MDR
Most Indian SMBs don't run a round-the-clock security operations centre — and don't need to build one from scratch. Sophos MDR is a fully managed detection-and-response service: expert analysts monitor, hunt threats and respond on your behalf, 24/7. Across Sophos' 35,000+ MDR customers, 99.98% of threats are stopped automatically, with average response times of under 1 minute to detect, under 25 minutes to investigate, and under 12 minutes to respond.
It comes in two tiers:
| Capability | MDR Essentials | MDR Complete |
|---|---|---|
| 24/7 expert-led threat monitoring and response | ✓ | ✓ |
| Detection & response across endpoint, network, cloud, identity, email, productivity, backup | ✓ | ✓ |
| Proactive threat hunting | ✓ | ✓ |
| Direct call-in support during active incidents | ✓ | ✓ |
| Root cause analysis | — | ✓ |
| Full-scale incident response (threats fully eliminated) | — | ✓ |
| Dedicated incident response lead | — | ✓ |
| Sophos breach protection warranty | — | ✓ |
MDR for Microsoft environments
If your business already runs on Microsoft 365, this is worth a special mention: Sophos MDR includes a Microsoft-specific service delivered by Microsoft Certified Security Operations Analysts, with deep two-way integration into Microsoft 365 and Microsoft Graph Security. Rather than just alerting you, Sophos analysts can act directly in your Microsoft tenant — revoking Microsoft 365 sessions, disabling compromised sign-ins, suspending malicious inbox rules — across any plan from Business Basic through E5. It's a Microsoft-verified solution through the Microsoft Intelligent Security Association (MISA) and a Gartner Peer Insights Customers' Choice for Managed Detection and Response.
If you're currently trialling Microsoft 365 Copilot (see our Copilot in 30 guide), MDR for Microsoft is a natural pairing — Copilot puts more of your business data in reach inside Microsoft 365; MDR for Microsoft is what watches that same environment around the clock.
One console for everything: Sophos Central
All of the above — firewall, ZTNA, endpoint, XDR, MDR, email, cloud — is managed from a single console, Sophos Central, organised across five pillars: SecOps, Endpoint Security, Network Security, Cloud Security and Email Security. The payoff is Synchronized Security: when one product detects a threat, it shares that signal instantly with the others, so a compromised endpoint can automatically trigger the firewall and ZTNA gateway to restrict its access — without a human having to correlate alerts across five different dashboards first. Sophos backs this with global scale: 600,000+ customers, 250+ dedicated threat-intelligence researchers (Sophos X-Ops), and 223+ terabytes of telemetry processed daily.
Where to start: Sophos Advisory Services
Not every business is ready to jump straight into a new stack — sometimes the right first step is finding out where you actually stand. Sophos' advisory services cover exactly that:
| Assessment | Focus | Answers |
|---|---|---|
| External Penetration Testing | Internet-facing systems — websites, VPNs, public services | What can an attacker see and access from outside? |
| Internal Penetration Testing | Systems, applications and data inside the network | What could an insider or a foothold attacker reach? |
| Wireless Network Penetration Testing | Wi-Fi infrastructure, encryption, authentication | Is the wireless network secure? Any rogue access points? |
| Web Application Security Assessment | Coding flaws, authentication, session management | Are customer-facing apps and portals exposed? |
For a lot of SNA's customers, this is the practical entry point: a focused assessment first, then a right-sized combination of firewall, ZTNA, XDR or MDR based on what it actually finds — not a blanket sell of every product in the portfolio.
Good news for government and PSU buyers
Sophos Endpoint, Sophos XDR and Sophos MDR now qualify under Make in India / ESG criteria. For public-sector buyers procuring through GeM, that's a real, verifiable point in favour of a Sophos-based security stack — relevant to the government and PSU work SNA already handles through its Government e-Marketplace (GeM) practice.
Why build your Sophos stack with SNA Infotech
Since 1989, SNA Infotech has helped Mumbai businesses put the right security in place — not the most expensive one. Our cybersecurity practice is built around Fortinet and Sophos, and the same team that runs your firewall, XDR or MDR engagement is the one that already manages your IT infrastructure, so a security incident doesn't become a finger-pointing exercise between vendors. Whichever piece you start with — a penetration test, a firewall refresh, or handing off 24/7 monitoring to MDR — we scope it around what your business actually needs.
Not sure which piece of this you need first?
Call us on +91 90040 86541 / +91 90040 86543, WhatsApp +91 86910 41556, or email mktg@sna-infotech.co.in to book a security assessment with SNA Infotech.
Book a Security Assessment →